ASRS Ltd provides 24/7 security operations services. Our team and partners are constantly developing new tools and appliances, permanently evaluating what is happening in your digital environment, mitigating current threats and new incidents.
ACTIVE MONITORING
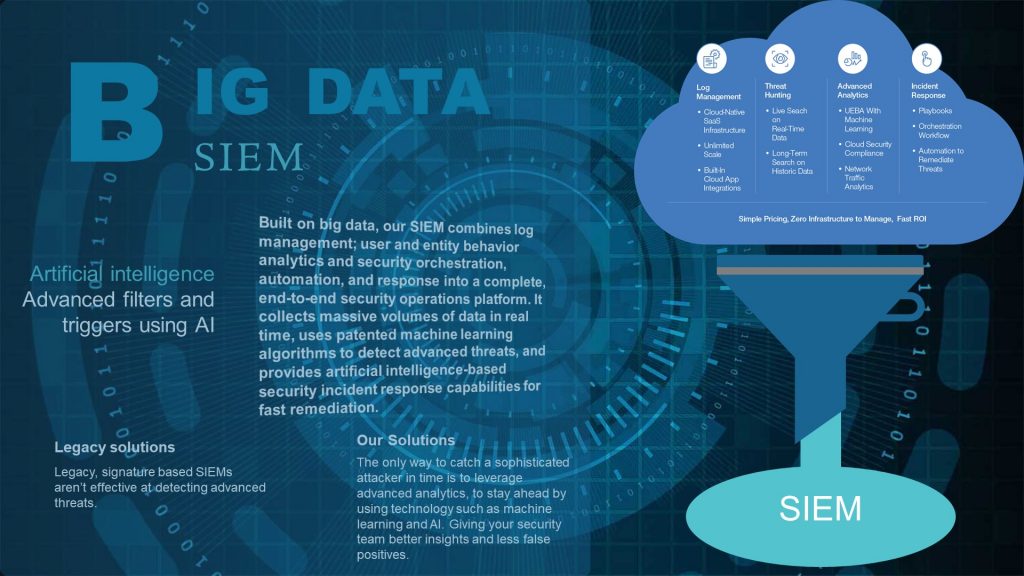
- Managed service, which uses a combination of automated analysis (advanced tools) and human intelligence to detect breaches and vulnerabilities.
- Logs, events and registries are collected from all connected devices, then encrypted and transported for analysis.
- We provide detailed and visualized information on the threats and measures taken to prevent breaches / data theft.
- Our service makes sure you are safe and free to focus on your core business while we take care of your security.
Basic steps
1. COLLECTING
Monitoring agent will be installed in all network devices and servers. This agent is a piece of software, which collects logs and events and sends them to an encrypted box.
2. SECURE TRANSPORT
A physical or virtual encryption box is connected to the client’s IT infrastructure. Designed to transport logs in a secure way (every file is encrypted using AES 256-bit encryption in diverse locations) through the Internet into a Security operations center (SOC).
3. ANALYSIS & ACTION
SOC is the main part of the protection plan and data protection system that reduces the level of exposure of information systems to both external and internal risks. It takes a crucial role in our solution because it is the place where the alarm goes off for every suspicious behavior. In the SOC, logs are analyzed on two levels. The first one is automatic analysis, which is constantly improving and adapting AI powered tools to extract and ease SOC operators. The second and most important level is manual analysis, done by our certified IT security specialists. Reports of issues or breeches are given instantly to our customers. The serious incidents are isolated in the SOC. Some customers prefer the ultimate solution from us, including an additional emergency response team 24/7 active second level support, which analyzes the incident deeply, blocks the attacker, stops the spreading, collects all the evidence, and helps to recover.
SOC SPECIFICATIONS
- Highest security requirements according to ISO/IEC 27000, NIST
- Creates the core of our solution
- 24/7 monitoring
- Immediate response time
- Full reports, understandable for non professionals
BENEFITS
- Saving time, money and human resources
- Certified and highly skilled personnel
- Real-time monitoring
- Immediate response
- Understandable reports to the management of the company
- Vulnerability management